Intelligent Repository Analysis

See which vulnerable dependencies your code calls, and where.

Integrate your GitHub repositories or Upload a Zip file. Zero code run. Dependency Map matches every direct and transitive dependency to known CVEs, then traces each one to the function and line in your code that uses it. Fix the reachable ones first.
searchScan Your Repository
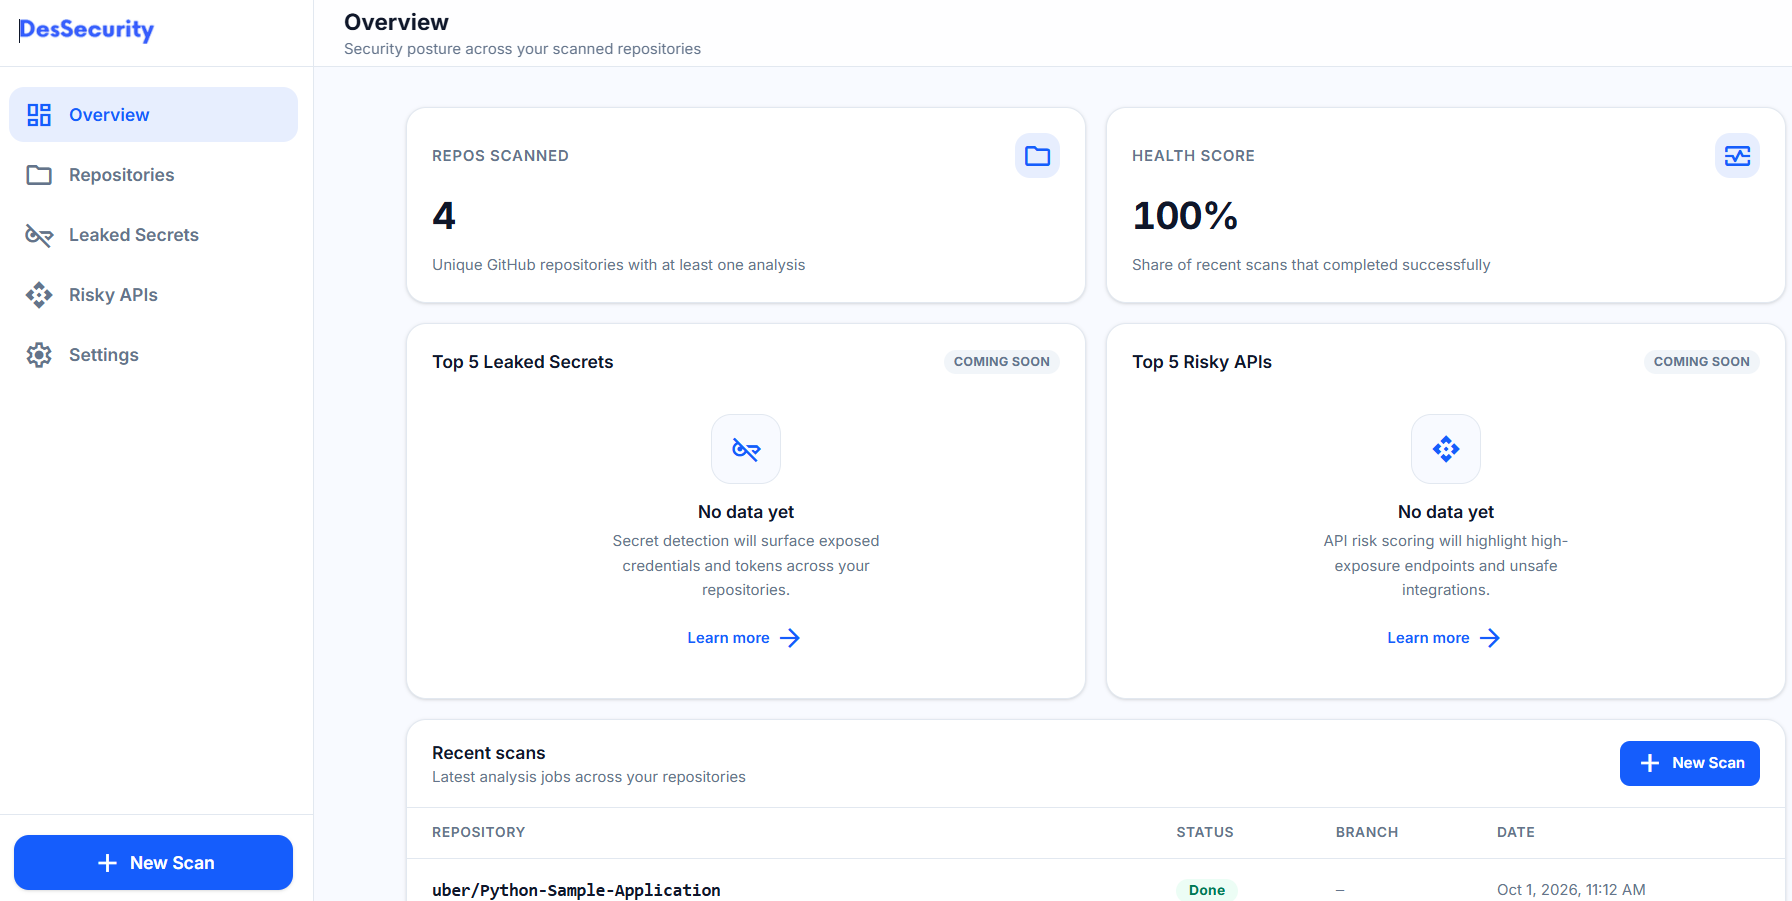
Dashboard Overview showing interactive dependency graph and security score

Comprehensive Security Toolkit

Everything you need to secure your dependencies in one intelligent platform.

hub

Dependency Graph

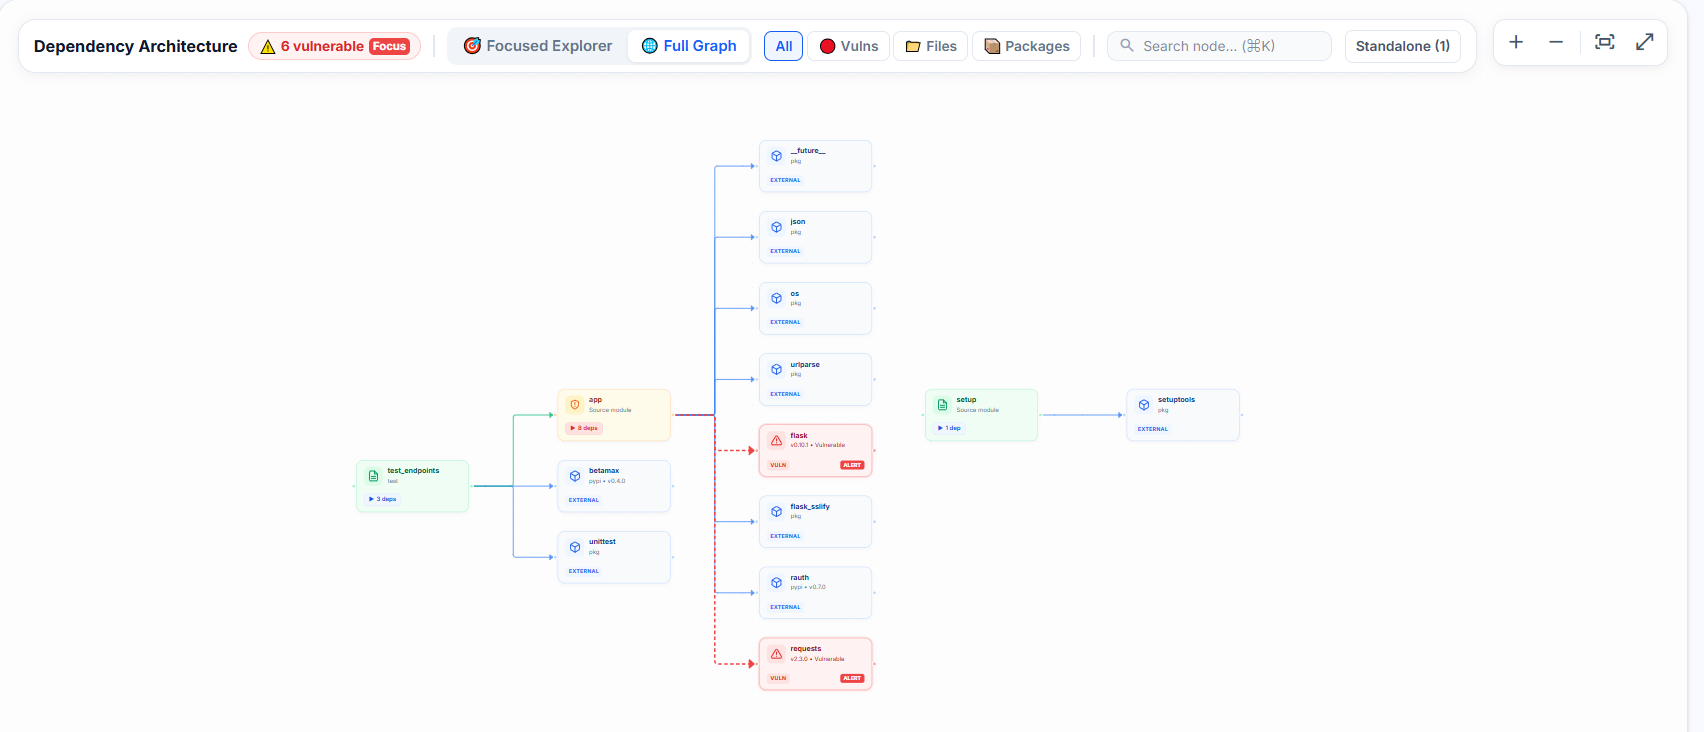
Visualize complex dependency trees and understand the blast radius of potential vulnerabilities instantly.

shield

Vulnerability Detection

Automated scanning against global CVE databases to flag critical issues before they hit production.

schema

Architecture Visualization

Map out your software architecture dynamically to see exactly where services connect and data flows.

emergency_home

Risk Management

Score and prioritize CVE findings by blast-radius impact so your team always fixes the highest-risk dependency first.

app.dessecurity.com/architecture
Detailed software architecture visualization dashboard showing active vulnerabilities and total dependencies
account_tree
AST Dependency Mapping

Understand your dependencies

Gain crystal-clear visibility into both direct and transitive dependencies. Automatically map your entire software supply chain surface area with zero code execution.

express→body-parser@1.20→bytes
shield_locked
CVE & Reachability

See which CVEs your code actually reaches

Every dependency is matched against known CVEs, then traced to the function and line that calls the vulnerable code. Reachable findings rise to the top; anything we can’t confirm is marked unconfirmed, never silently dropped.

CVE HighCVE-2024-21538
Reachable
scripts/build.js:42 · runBuild()7.5 CVSS
key
Risky APIs & Secrets

Catch risky calls and leaked secrets

Flags command execution, eval, SQL, deserialization and SSRF calls in your own code, marking the ones fed by request data. Finds committed API keys and tokens, and checks whether each still works. Only a masked preview is stored.

APIchild_process.exec · CWE-78User input
SecretAWS · AKIA••••••••3F7QLive
speed
Prioritization

Risk Scoring

Findings are ranked by one risk score, so the highest-impact vulnerabilities come first.

1lodashCritical
2axiosHigh
3minimistMedium

Start securing your repositories today.

Join leading security teams who trust desSecurity to monitor, analyze, and protect their critical codebases.