About DesSecurity
Repository security that respects your time.
We help security teams see what their code actually depends on — every package, every function, every CVE — without installing agents or waiting hours for a scan. Our goal is to make dependency security as fast and clear as linting your code.
What we believe
Fast feedback
A scan finishes in minutes, not days. If it takes longer than a lint run, developers won’t use it.
Honest signal
We never hide uncertainty. Every finding carries a confidence level so you know what’s guessed vs. verified.
Zero install
No agents, no SDKs, no changes to your pipeline. Point us at a GitHub repo and we return results.
Founder
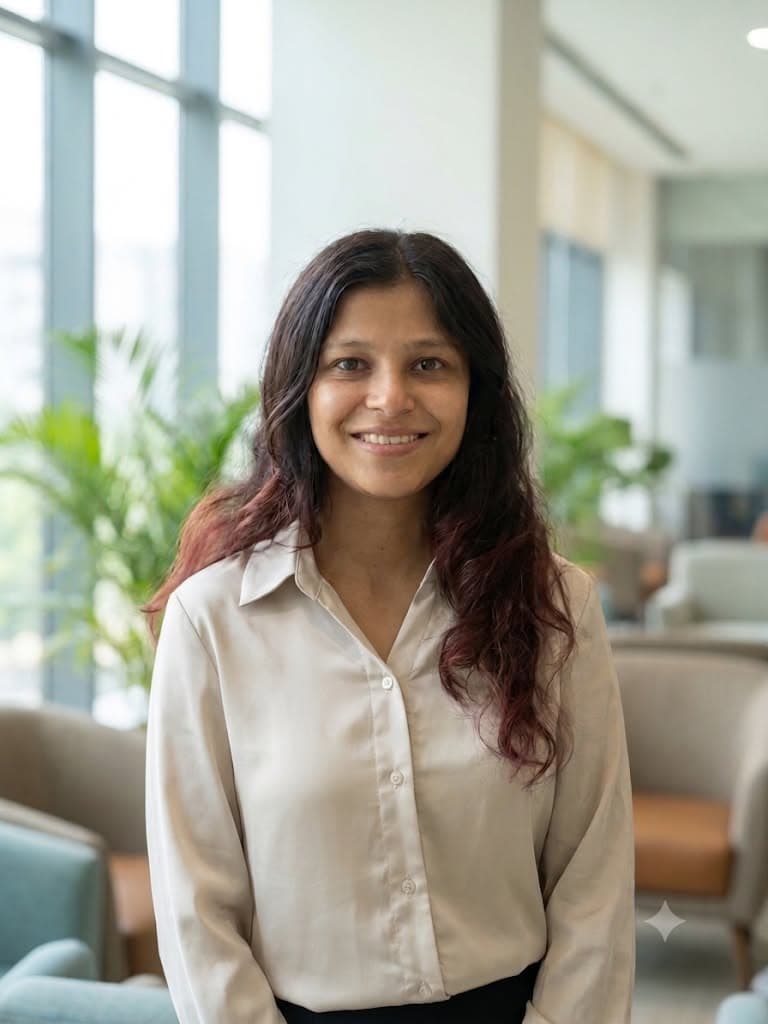
Kshitija Kulkarni
LinkedInFounder
Cybersecurity engineer with 4+ years across security operations, cloud security (AWS/Azure), Kubernetes, and CNAPP tooling.
I started desSecurity after watching teams drown in CVE noise — thousands of findings, no reachability, no way to tell what mattered. Dependency Map is the tool I wished existed: it reads your code, maps every dependency to the functions that actually use it, and tells you which vulnerabilities you can safely defer. The result is triage in hours, not weeks.
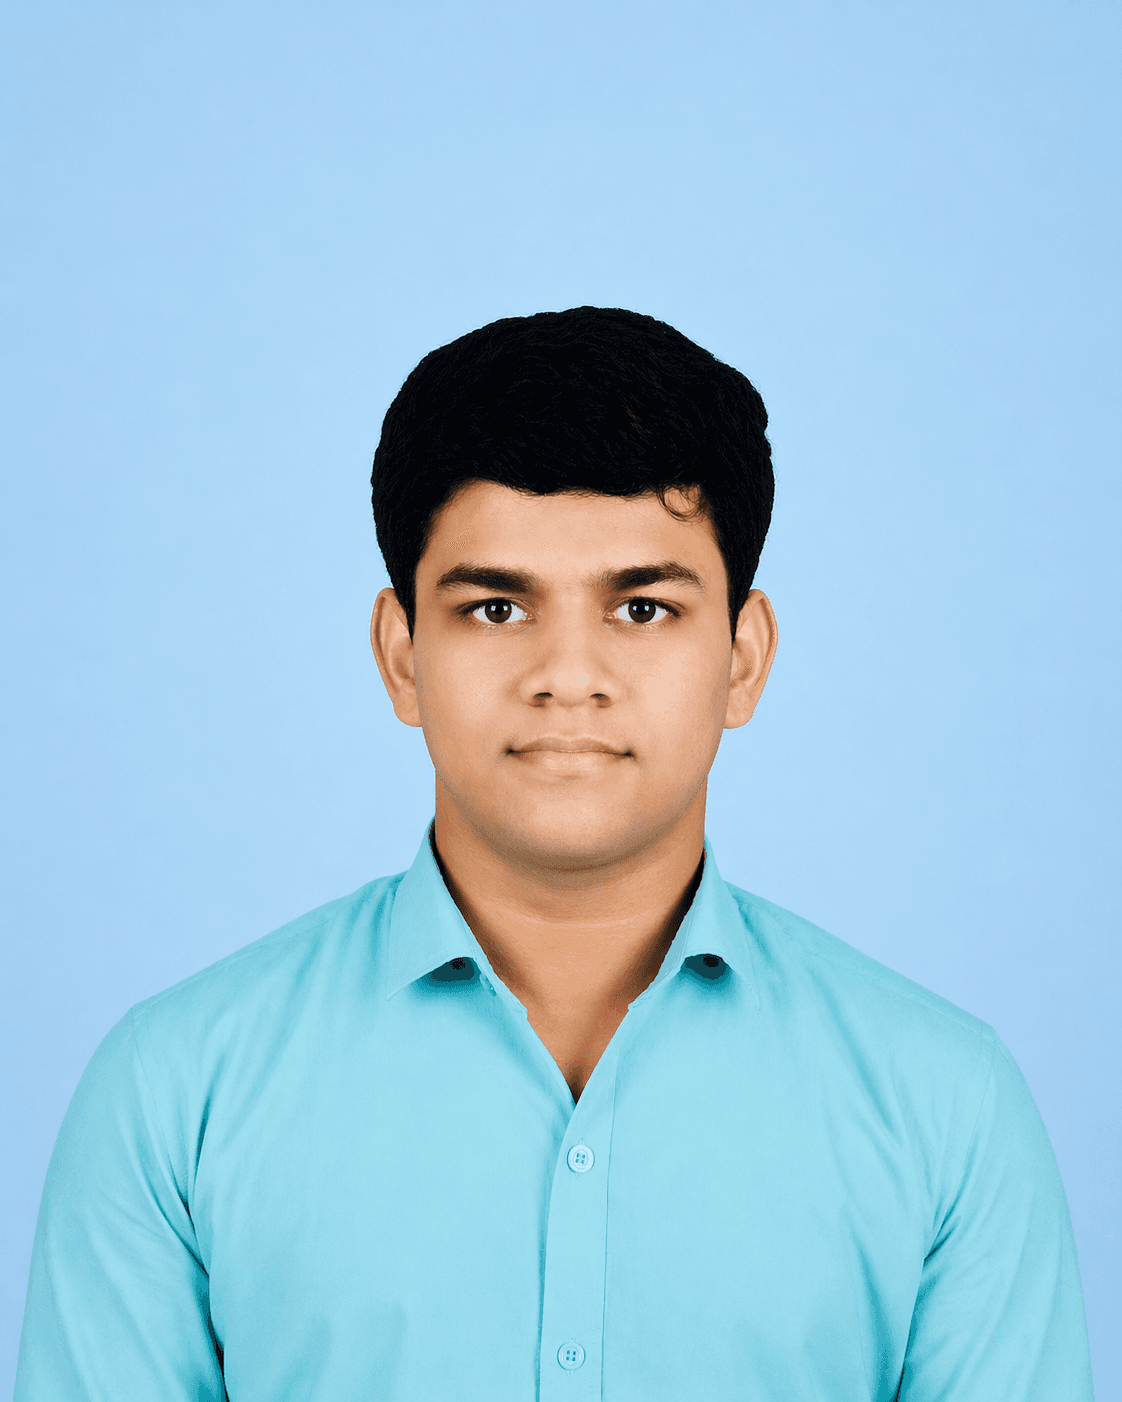
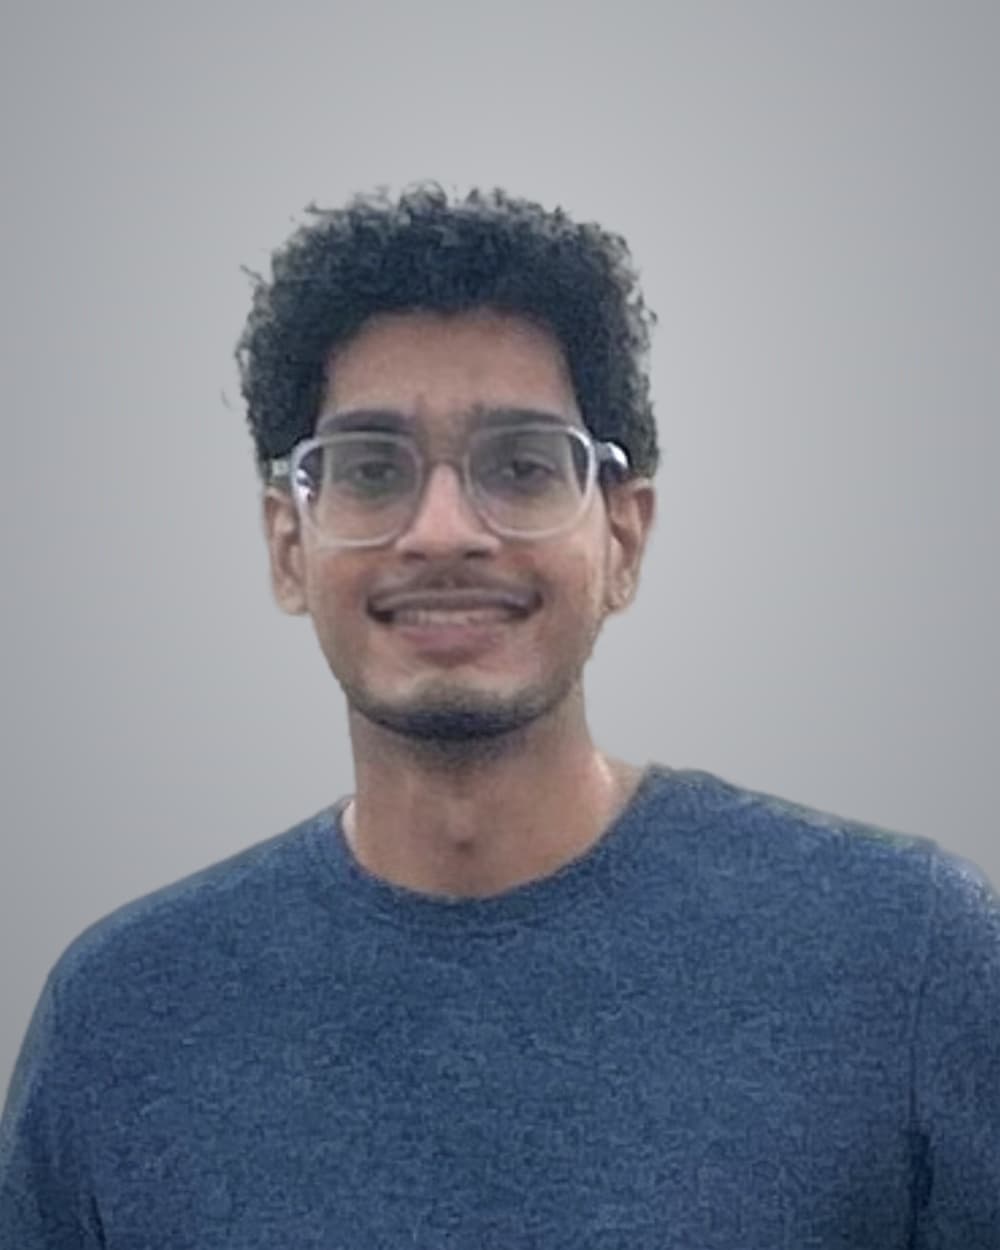
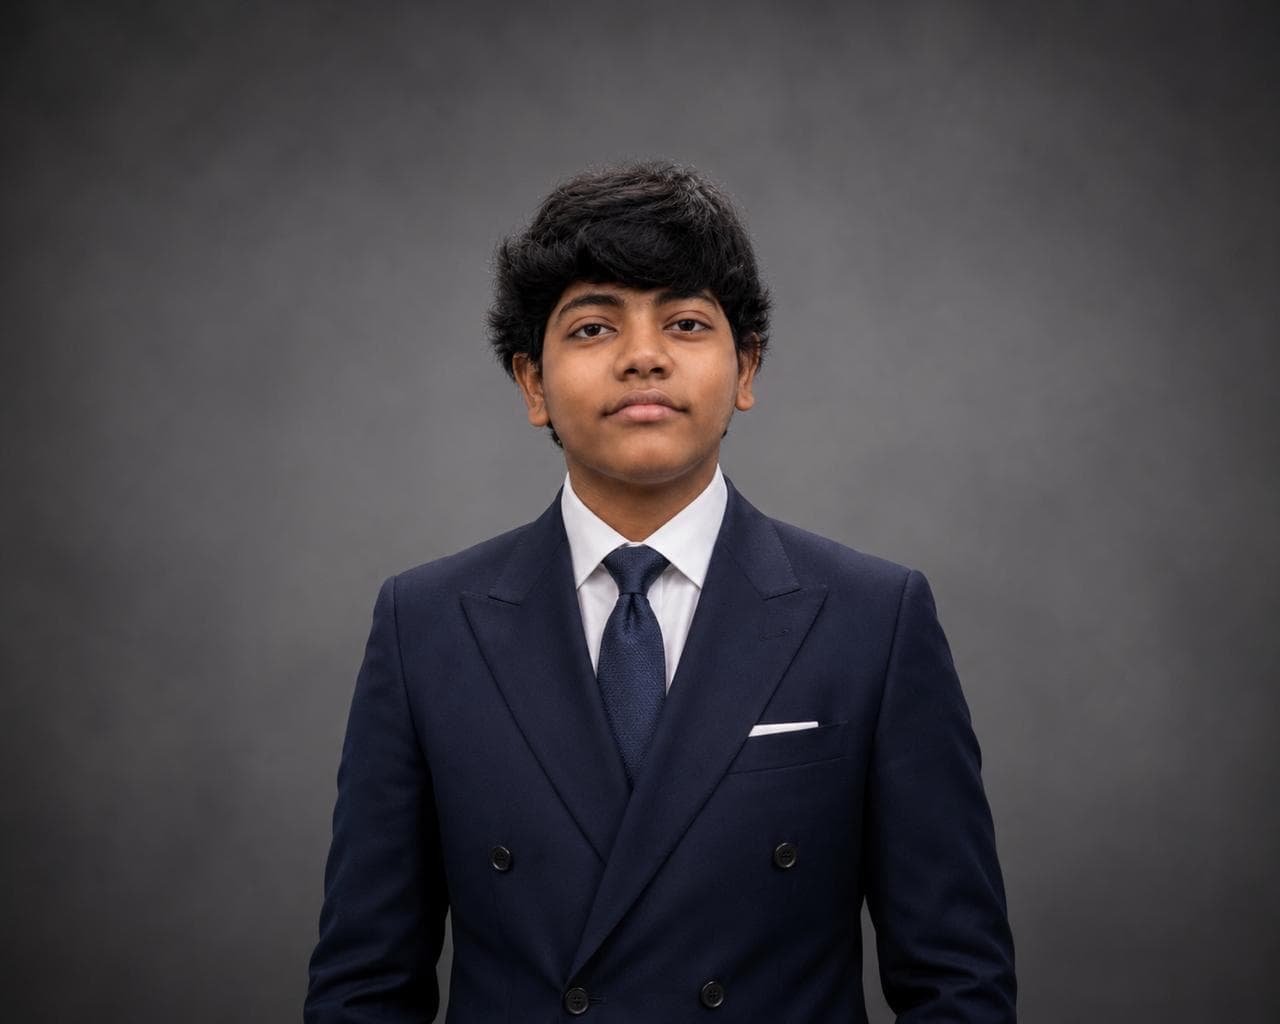
The team
Want to see it in action?
Point Dependency Map at a GitHub repo — public or private — and get a complete security picture in minutes. No install, no agents, no credit card.
searchScan a repository